Universal Phygital Edge Compute
Moving from single-purpose, capital-intensive terminals to a unified, multi-tenant edge node. Powered by the Salient FinTech Innovation Set as its foundational trust engine, competing tenant workloads share the same hardware while maintaining total logical, network, and cryptographic isolation under the Constitutional OS (seL4 microkernel + TPM 2.0/HSM enclaves). Peripherals communicate via the secure CEN XFS4IoT standard, framing physical cash recycling, payment rails, and tokenised identity as the anchors of universal reach.
Seven Ranked Foundational Innovations
How physical silicon enforcement, TEE enclave isolation, and offline edge execution establish an impregnable phygital foundation for incoming tenant cohorts.
Authority Lives in the Agreement
Authority lives in the agreement, not in the identity. The POI appliance treats the bilateral agreement as the only source of authority: role granted → agreement authorises role → agreement decides case → cryptographic record proves execution.
Unlawful Execution is Unavailable
Unlawful execution is a state the platform cannot enter. The commercial word is insurable. The DRAGON hardware adjudication substrate intercepts edge stanzas before actuation, guaranteeing bounded operational loss conditions for tier-1 underwriters.
Constitutional Delegation & Agent Liability
Edge AI models and automated robotic actuators execute under signed On-Behalf-Of (OBO) delegation tokens with single-action expiry and pre-ruling GateKeeper verification, preventing hallucinated scope creep.
Lawful Execution at the Counter
Pre-execution adjudication runs locally on the POI appliance hardware at the physical counter. The platform settles and validates transactions during power cuts and broadband partitions without cloud backhaul, ensuring public-interest civic resilience.
Many Tenants, One Appliance
Multiple competing banks, retailers, healthcare providers, and civic authorities run on a single physical POI node. Hardware-isolated TEE enclaves and seL4 microkernel separation eliminate cross-contamination and slash hardware deployment capex.
Flat Clearing & Sovereign Wallet
Deterministic agreement execution enables direct A2A / SEPA Instant clearing at a predictable flat target clearing fee (near-term target state architecture, Q4 2026 / 2027 roadmap). oneWallet acts as the sovereign root of authority projecting verifiable micro-claims.
 Strategic Lever 01
Replay as a Product, Not a Log
Re-run hardware decisions exactly as they were made, against the precise version of the rule in force at that exact millisecond.
 Strategic Lever 02
Switcher+ & Entitlement Continuity
Citizen entitlements and service histories travel with the user across disparate appliance endpoints without vendor lock-in.
 Strategic Lever 03
Institutional Standards Crosswalk
Native integration with CEN XFS4IoT peripheral standards, EMVCo C-8 contactless kernels, and BIAN Service Domains.
The Modular Compute Slab Paradigm
We reject the traditional model of constructing dedicated bank counters or single-purpose government desks. Instead, the platform deploys Universal Compute Slabs – edge processors running on the mathematically verified seL4 microkernel – whose capabilities are dynamically defined by the secure physical peripherals attached to them.
By routing peripheral hardware via the network-attached CEN XFS4IoT standard and executing code inside hardware-isolated enclaves, a single physical kiosk can securely host competing workloads. Cash recycling and advanced peripherals act as the physical anchor of universal reach, fulfilling the "leave nobody behind" mandate, while mobile wallets serve as the user interface.
As digital services accelerate, physical presence collapses – creating vast "Service Deserts". Shared phygital infrastructure addresses the "Three Zeros" (Zero Data, Zero Power, Zero Device), ensuring inclusive access to digital commerce and government.
Pace-Layered Application Strategy
The platform separates the immutable System of Record (SoR) from the agile System of Engagement (SoE). Tenants develop rapid UI innovations at the edge, while core security and transactional compliance are locked in hardware circuits.
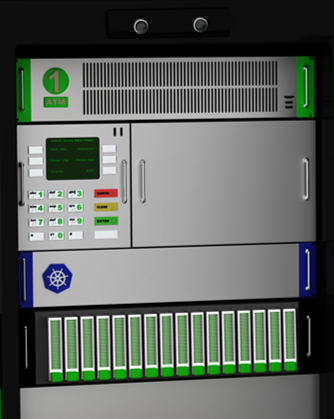
Hardware should be explicit, not mystical: The POI edge node acts as a replaceable infrastructure component. Standardised rack/slab enclosures decouple compute from the industrial chassis, isolating seL4 microkernel processors, TEE accelerators, and bus controllers from the harsh physical environment while ensuring wire-speed peripheral interception.
1. Confidential Computing Enclaves (AMD SEV-SNP)
Multi-tenant workloads run within hardware-isolated Trusted Execution Environments (such as AMD SEV-SNP or Intel SGX). Data in use remains encrypted in memory, preventing physical or host-level memory snooping across tenant boundaries.
2. SmartNIC DPUs & Kernel-Level eBPF Interception
Network traffic and inter-service calls are intercepted at the kernel level using eBPF and Cilium on SmartNIC Data Processing Units (DPUs). Abnormal telemetry triggers the Emergency Constitutional Alert Protocol, dropping unauthorised packets at wire speed.
3. Cryptographic HBOM Attestation & Bus-Level Lockout
Every peripheral module (smart-card readers, biometrics) presents a verifiable cryptographic passport. During system bootstrap, DRAGON evaluates the HBOM digest. If an unmapped peripheral identifier is detected on the serial peripheral interface (SPI) or PCIe bus lines, or if firmware deviates, a hard hardware interrupt locks execution at the silicon level before memory contamination can occur.
4. On-Behalf-Of (OBO) Delegation Tokens
Edge interactions initiated by AI agents or local operators require an OBO token bound to a single-use Delegation DAG. This restricts edge execution authority to a specific purpose, maximum cost ceiling (\(F_{\text{Cost}}\)), and time window (\(O_{\text{SunsetDate}}\)), preventing privilege escalation.
Day One in a Governed Community Service Hub
The Tenant Shell dynamically loads branded micro-frontends via a unified API. From the merchant's perspective, day one introduces new services and instant cashflow optimisation.
What the Merchant Sees
Enterprise-Grade, Always-On Device
A single appliance replaces multiple legacy terminals. Branded interfaces load dynamically for customers, while software updates and compliance patches happen automatically over the air.
New Revenue Streams
Earn commissions on cash deposits and withdrawals, bill payments, digital identity registrations, and parcel collections processed through the node. Physical floor space is structurally turned into a transaction hub.
Instant Working Capital
Sales are ledgered in real time on the System of Record, unlocking immediate access to credit union capital and overdraft facilities, bypassing traditional credit application loops.
The Pharmacy Scenario – Phygital Service Arbitrage
Customer Journey Lifecycle
A customer authenticates at the kiosk using their biometrically verified oneWallet.online identity profile.
They apply to switch their services via Switcher+, opening a new bank account on the credit union tenant's secure runtime.
The kiosk scans and verifies their identity documents, validating them against the national civil registry.
They withdraw cash from the integrated CICO recycler to complete a prescription co-payment with real-time settlement.
The kiosk dispenses their cards and SIM, while a smart locker releases their medication – earning the pharmacy a transaction fee.
Before – Standalone Merchant
- High transaction processing fees with T+3 settlement.
- Costly, single-purpose payment acceptance terminals.
- Zero store foot traffic generated from community services.
- No structural visibility to secure instant working capital.
- Heavy compliance burden and manual record management.
After – POI Network Member
- Low-cost transactions using A2A rails and SEPA Instant.
- One physical node hosts banking, shipping, and retail workloads.
- Earn transaction fees from deposits, identity, and parcel delivery.
- Real-time ledger data enables instant capital availability.
- Inherent compliance – data is verified and proven at the edge.
The Pervasive Sensory Capture Substrate
By pooling multi-tenant capital, the platform makes high-assurance physical verification peripherals a standard, universally shared community asset, bringing institutional-grade security to the extreme edge.
Multi-Spectral Document Imaging Core
Standard phone cameras are highly vulnerable to digital or high-resolution paper print forgeries. The Switcher+ document imaging core deploys an uncompromised dual UHD lens stereoscopic array that evaluates document security marks across several light wavelengths:
- Visible Light: Captures high-res lexical parameters for OCR layout mapping.
- Ultraviolet (UV) 365nm: Excites hidden fluorescent fibres, microprints, and security thread matrices.
- Infrared (IR) 950nm: Penetrates surface inks to verify underlying raw security paper substrate.
Full hardware specification and capture path schematics are available to qualified partners following the Discovery Sprint engagement.
Remote Teller Assist (RTA): Hardware Peripherals & Virtual Teller Automation
Deploying dedicated human teller staff at every distributed community location is economically non-viable; conversely, forcing complex life-event transactions into sterile self-service interfaces leads to high transaction abandonment. The onePOI Remote Teller Assist (RTA v3.1) architecture unifies high-assurance CEN XFS4IoT peripheral control with sovereign, encrypted video teller telepresence. When an assisted self-service workflow is triggered, remote licensed banking officers are dynamically teleported into a hardware-enforced WebRTC session. The officer can remotely inspect multi-spectral document scans, verify biometrics, and guide cash recycling or card dispensing – all constrained by strict TEE hardware enclaves with zero access to plaintext customer credentials.
Packaged Business Capabilities (PBCs) at the Edge
The POI appliance transforms physical hardware modules into reusable, contractually bound Packaged Business Capabilities (PBCs). Cash recyclers, card dispensers, stereoscopic document scanners, and biometric sensors are decoupled from monolithic software, allowing multi-tenant services to be provisioned on demand.
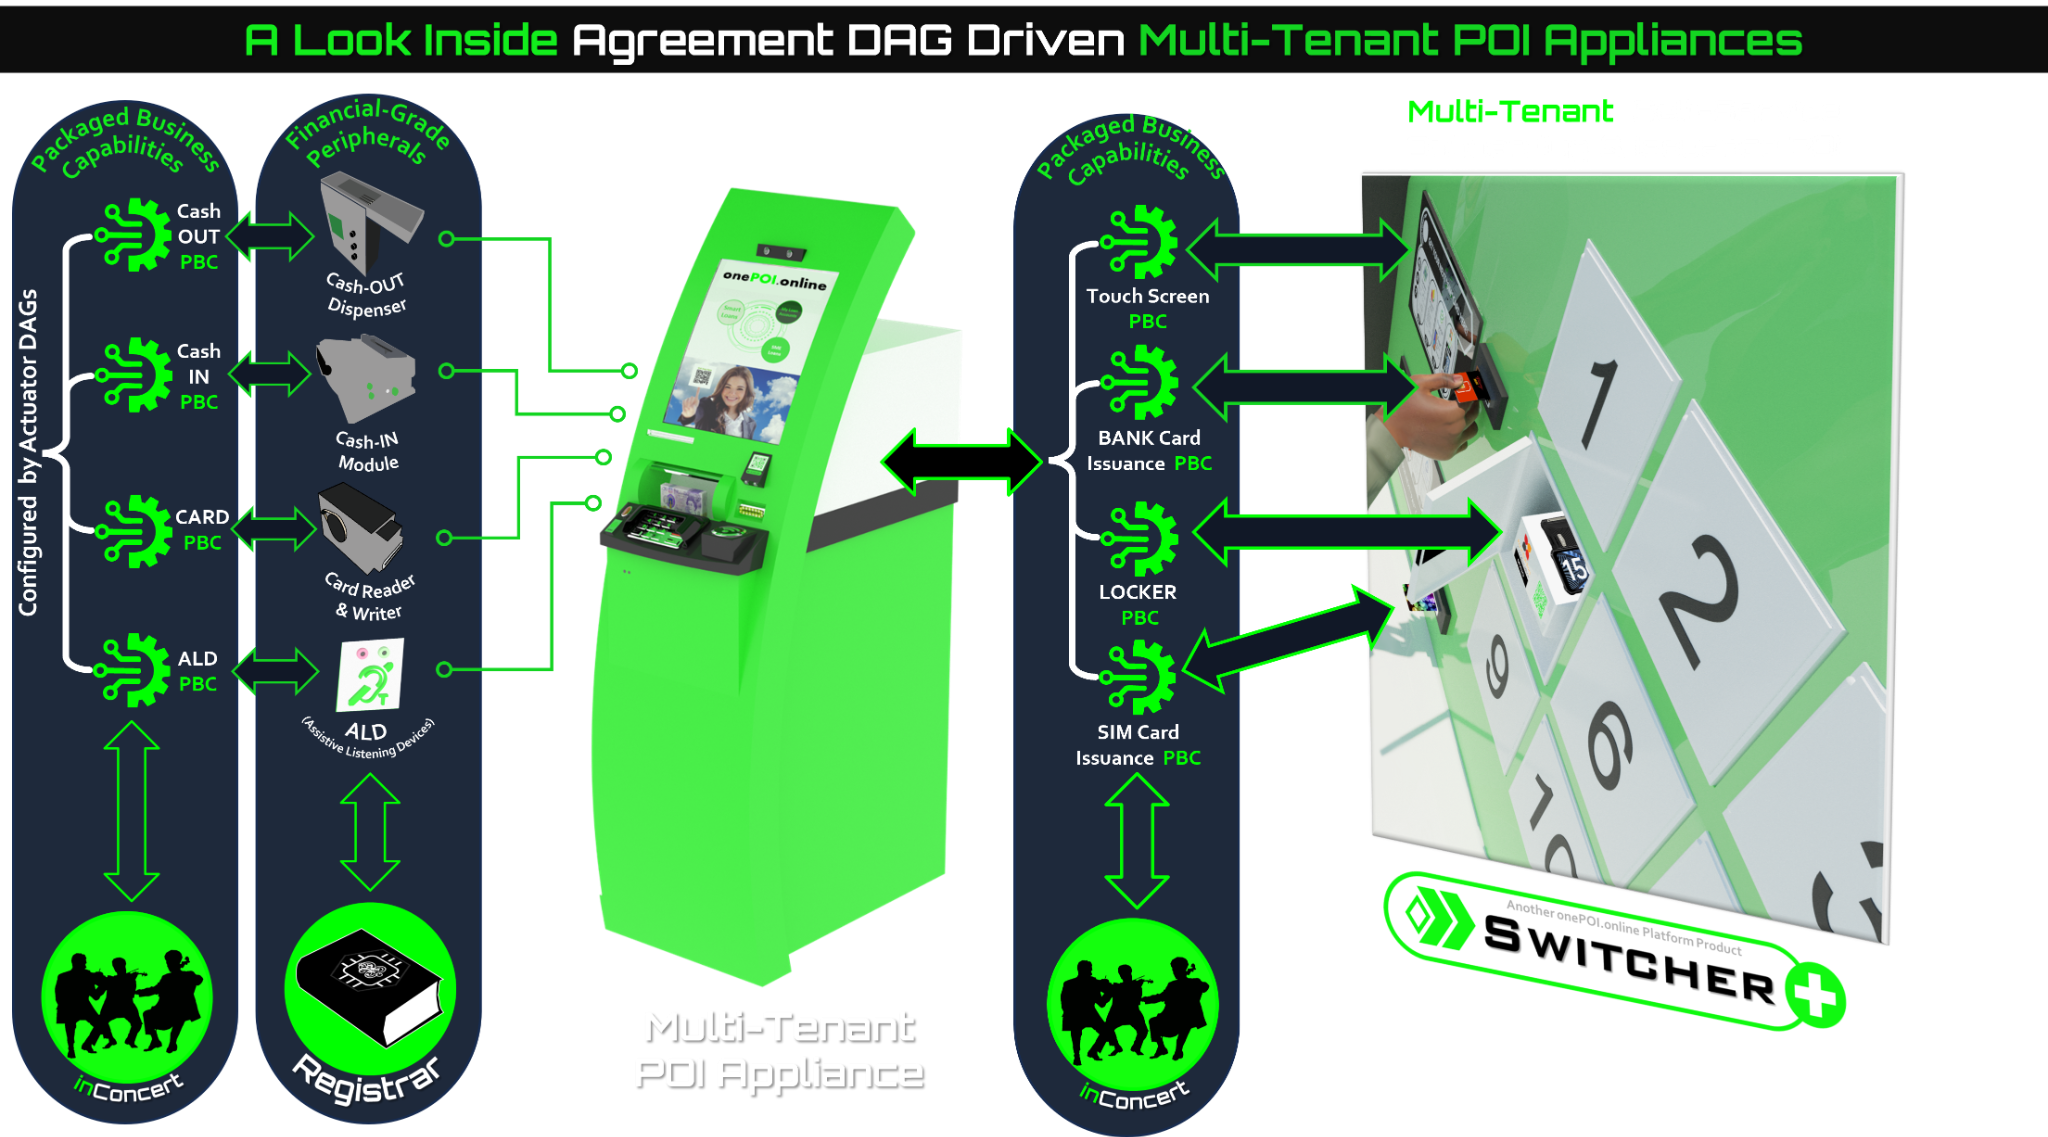
Multi-Peripheral Coexistence
Cash-in, cash-out, card read/write, document capture, card issuance, and secure locker hand-off coexist through Switcher+ and governed orchestration. The appliance evolves incrementally with community demand rather than requiring costly estate-wide replacements.
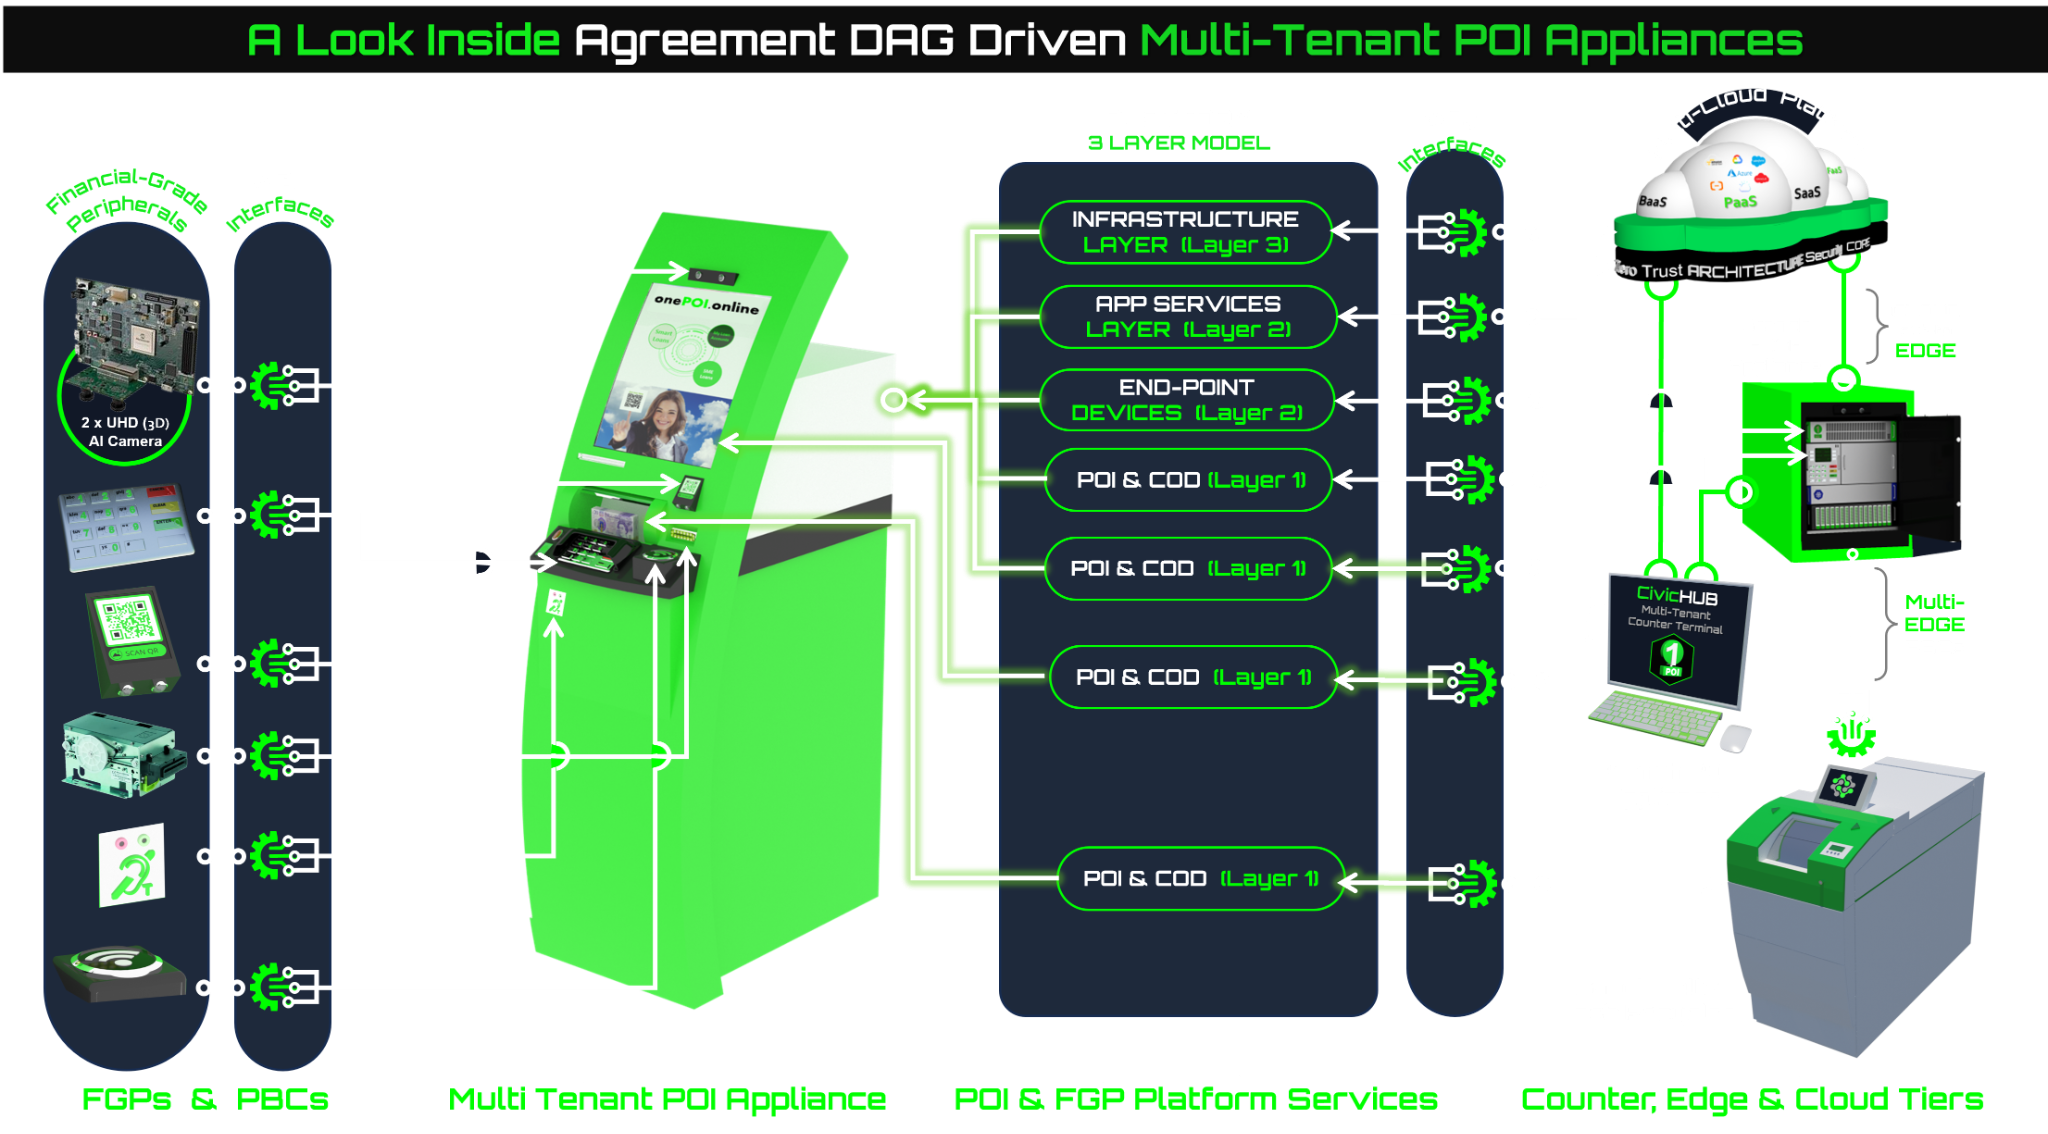
A Continuum Across Device, Edge & Cloud
PBC interfaces mediate between physical peripherals, appliance micro-services, and remote cloud systems. Hardware components can be updated or replaced without rewriting tenant business logic, ensuring vendor independence and brownfield longevity.
The Switcher+ Agentic Concierge
In the canonical execution hierarchy: iEngine proposes, DRAGON adjudicates, Conductor executes, Switcher+ fulfils. Switcher+ is the operational edge fulfilment channel of the System of Orchestration (SoO), transforming high-friction onboarding, service switching, and device lifecycle management into a secure, unified phygital experience.
Ingress & Photoplethysmography (rPPG) Pulse Scan
Standing at the kiosk with zero credentials, Sarah touches the activation panel. The appliance initialises a 3D NIR camera to project a geometric coordinate contour map of her face. Concurrently, an invisible rPPG sensor captures minor cardiovascular skin-colour changes to verify her live blood-flow, blocking a 2D deepfake video playback attack in milliseconds.
oneWallet.online Integration
Identity is the absolute cornerstone of financial risk management. oneWallet.online provides the secure digital key to the entire ecosystem, fully compliant with eIDAS 2.0 and EUDI Wallet standards.
The Digital Twin of the Document (DToD)
Rather than storing static credentials, the wallet manages the user's Personal Knowledge Graph (PKG) and coordinates their Zero-Party Data (ZPD) perimeter. When an e-Passport is scanned, the data is transformed into a secure DToD container.
To satisfy the conflict between GDPR deletion rights and anti-money laundering (AMLR) retention rules, the platform switch-points utilise Cryptographic Shredding. Raw personally identifiable information (PII) keys are stored in secure TEE enclaves and destroyed upon request, rendering raw data unreadable while keeping zero-knowledge (ZK) compliance markers intact on the ledger.
Agentic Consent & Neuro-Symbolic Sandwich
AI agents possess Zero Standing Privileges. Their operations are strictly isolated by short-lived On-Behalf-Of (OBO) Tokens. The edge appliance enforces the Neuro-Symbolic Sandwich – probabilistic AI (via iEngine) proposes actions, while the deterministic DRAGON adjudication substrate validates them against hard constitutional rules, Conductor executes, and Switcher+ fulfils.
Real-Time Consent Revocation Cascade
When a user revokes access permissions, the system registers a Sovereign Act, re-mints the global Policy Hash, and propagates the state platform-wide via Atomic Map Updates. Active sessions violating the updated policies are terminated in milliseconds.
Transforming GRC from a Regulatory Cost into a Liquidity Engine
Fusing corporate and statutory compliance directly into hardware circuits does more than mitigate liability – it fundamentally optimises the enterprise balance sheet under Basel IV guidelines.
Basel IV OpRisk Capital Release
Because operational risk is structurally contained at the hardware gate via non-repudiable LAHEs, banks can petition regulators for an immediate reduction in their Internal Loss Multiplier (ILM), releasing locked, non-earning capital.
Phygital Service Arbitrage
By sharing a physical POI footprint across a Tenant Cohort, high-margin commercial transactions effectively cross-subsidise low-margin civic interactions, making community hubs highly profitable.
Where the Business Indicator (BI) tracks gross revenue streams, and the Internal Loss Multiplier (ILM) is derived from historical loss event counts – which COS compresses to near-zero.
Micro-3PL, Edge MEC & Teleportation Architecture
Bridging high-assurance mechatronic edge hardware, resilient hybrid connectivity, and hardware-authenticated remote service control for micro-marts and civic hubs.
Micro-3PL & Locker Hardware
Features dual UHD 3D AI stereoscopic cameras for volumetric payload inspection, CIT-grade secure solenoid access doors, and 2-way rear-loading pass-through modules for civic hubs and micro-marts.
Base Station / Edge MEC
Integrated Multi-access Edge Compute (MEC) node with 5G/Wi-Fi private network slicing and LEO satellite access gateways, ensuring continuous offline resilience in rural deployments.
Peripherals & Accessibility
Native interface for Assistive Listening Devices (ALDs), magnetic induction loops, tactile Braille keypads, and modular smart card reader/writer Packaged Business Capabilities (PBCs).
Clerk Teleportation
Allows remote bank or civic clerks to take hardware-authenticated, low-latency control of edge POI Appliances via WebRTC over WireGuard, subject to real-time DRAGON audit logging.
POI Appliance Multi-Tenant Execution
Details the physical boundaries, fail-closed state machines, and attestation protocols that define edge hardware governance.
Deterministic Rule Execution
The POI Appliance guarantees the execution of programmed rule stanzas as written directly at the transistor level. It does not judge the moral or strategic quality of the rules themselves – that responsibility remains strictly with human constitutional authors (TopHAT).
Edge Failure & Active VETO
If hardware failures occur – such as an XFS4IoT shutter jam or dispenser lock failure – the DRAGON adjudication substrate issues an immediate VETO. This prohibits autonomous AI inference from resolving states, forces a fail-closed condition, and triggers a high-priority $O\_Audit$ record for TopHAT expert review.
Continuous Attestation (cATO)
Boot registers and platform configurations are continuously measured against cryptographically signed bills of materials (xBOMs). If a configuration drifts from the registered baseline, the TPM 2.0 locks the session keys and alerts the Registrar.
Salient FinTech Innovation Set
The Sovereign Trust Engine at the Core
The overarching framework is the Salient Innovation Set. At its foundational core lies the Salient FinTech Innovation Set. Every phygital, civic, healthcare, retail, or agentic interaction ultimately resolves into a lawful value exchange, identity binding, cryptographic settlement, or fiduciary obligation; therefore, the FinTech innovation set (BIAN bare-metal execution, real-time A2A rails, SEPA Instant, Token Gantry, bitemporal ledgers) provides the non-negotiable trust engine that makes the entire sovereign ecosystem viable for all incoming Tenant Cohorts.
Rather than relying on closed proprietary payment networks with high toll extraction, the FinTech core executes bare-metal BIAN v14.0 Process Boundary Components, connects to direct account-to-account settlement rails, shreds plaintext credentials via Token Gantry, and preserves bitemporal evidence bundles that guarantee dispute-immune auditability across edge POI appliances.
BIAN v14.0 POS PBCs
Bare-metal Point-of-Sale Process Boundary Components. No proprietary POS middleware. No PCI-DSS scope creep.
Real-Time A2A Rails
PayShap and SEPA Instant Account-to-Account settlement. Target state architecture <500ms finality (Q4 2026 / 2027 roadmap). Zero interchange toll.
Token Gantry Identity
Card PANs replaced by cryptographic commitment tokens. Zero plaintext PII retained at any POI node.
Bitemporal Ledgers
Every transaction recorded in transaction-time and valid-time. Satisfies statutory dispute and audit timelines natively.
Field → Finance → Shelf → Neighbour
The POI Appliance is the hardware substrate every stage runs on, carrying value through each step and every tenant cohort.
Every stage of the continuum is served by a governed POI Appliance: the Class 5 smart box at the farm gate, the Class 3 banking and civic kiosk, the Class 4 logistics locker, the drive-through terminal. One appliance family, one constitutional layer, every stage.
Deploy Governed Phygital Infrastructure
For as little as €2,500*, a Discovery & Positioning Workshop evaluates your physical retail, banking, or civic estate against the Business & Tech Architecture and Constitutional Manifesto, delivering an actionable roadmap and hardware topology report before capital commitment.